Modes
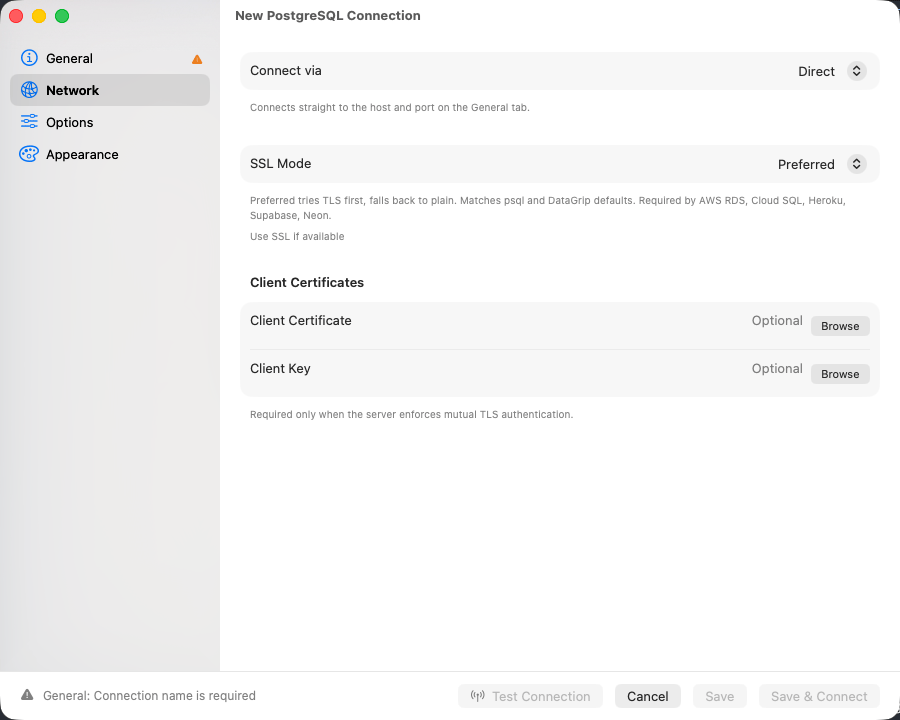
SSL mode and certificates below the transport picker
Certificate fields
The certificate rows appear only once SSL Mode is anything but Disabled. Each takes a file path, with Browse to pick one.
SQL Server shows no certificate fields at all and verifies against the system trust store. See SQL Server. Under Verify Identity, SAP HANA and Kafka verify against the system trust store when Certificate is left empty. See SAP HANA.
PostgreSQL, Redshift, CockroachDB and KingbaseES under Verify Identity with Certificate empty check the server against the roots this Mac trusts, as Keychain Access shows them, your own and your organization’s trust settings included. A
~/.postgresql/root.crt file, which libpq reads by default, is used instead when it exists. Backups and restores with pg_dump and pg_restore check the same way. Verify CA still needs the server’s CA certificate: libpq refuses it against the system roots, since anyone can get a public certificate for a host they control. A provider with its own CA, such as Amazon RDS or Supabase, still needs its CA bundle in Certificate.
Per-driver defaults
A new connection starts on the mode that matches the driver’s own default, and so does a connection URL that names no mode. The driver’s own guidance prints under the picker where there is any.Ports that mean TLS
Type one of these ports while SSL Mode is still at the driver’s default and the mode becomes Verify Identity, with a note under Port. Type a different port and the default comes back. A mode you picked yourself never changes.
A saved connection set to Disabled on one of these ports shows a warning under Port, with a button that switches it to Verify Identity. An imported URL follows the same rule; see Connection URL Reference.
Behind a tunnel
Verify CA and Verify Identity do not survive a tunnel. An SSH tunnel, Cloudflare tunnel, Cloud SQL Auth Proxy, or SOCKS proxy has the driver connect to127.0.0.1, and no server certificate is issued for that, so the mode drops to Required for the tunneled connection and the certificate paths are cleared. TLS itself still runs the whole way to the database; only the certificate check goes. If you need the check, reach the server without a tunnel.
On iPhone and iPad the check does survive an SSH tunnel: MySQL, MariaDB, PostgreSQL, Redshift, Redis and Oracle check the certificate against the host saved in the connection. An Oracle server saved as an IP address is still checked against 127.0.0.1, and Verify Identity refuses it.
Forwarding to a unix socket drops TLS altogether, because a socket cannot negotiate it. The SSH tunnel encrypts that path instead.
Troubleshooting
A TLS failure is reported with the cause, a mode to switch to, and the driver’s own response underneath, password redacted:“FATAL: no pg_hba.conf entry for host … no encryption”
The PostgreSQL server requires SSL and the connection is set to Disabled. Switch to Preferred or Required (skip verify).”SSL is required, but the server does not support it”
The MySQL or MariaDB server offers no TLS and the connection is set to Required or stricter, which never falls back to plain text. Turn on TLS on the server, or switch to Preferred to allow plain text.”Connections using insecure transport are prohibited”
The MySQL server hasrequire_secure_transport=ON. Switch to Preferred or Required (skip verify).
”SSL handshake failed” / “tls handshake failed”
Driver and server share no TLS version or cipher. Update the server, or on a development box drop to Required (skip verify).“certificate verify failed” / “self-signed certificate”
The server’s certificate chains to nothing in the system trust store. Set Verify CA and fill Certificate with the CA’s PEM, or drop to Required (skip verify) to skip validation.”hostname does not match certificate” / “Hostname verification failed”
The certificate’s CN or SAN does not cover the host you typed. Change Host to a name the certificate covers.”client certificate required”
The server enforces mutual TLS. Fill in Client Certificate and Client Key.”client private key is encrypted” / “passphrase is incorrect”
Enter the key’s passphrase in Key Passphrase, which appears once Client Key has a path. Trino, Presto and etcd have no Key Passphrase: decrypt the key first withopenssl pkey -in encrypted.key -out client.key and choose the decrypted file.
On iPhone and iPad
The Mac’s five modes, and Preferred does what the table above says for each driver. MySQL, MariaDB, PostgreSQL, Redshift, and Redis get CA Certificate, Client Certificate, and Client Key rows alongside them. Oracle gets Disabled, Preferred, Required, and Verify Identity with no certificate rows, so Verify Identity checks the server against the system trust store; an Oracle connection saved with Verify CA does not connect until its mode changes. SQL Server gets Disabled, Preferred, and Required. Each row takes a file or pasted text. Client Certificate also accepts a PKCS#12 (.p12 or .pfx) and fills in both the certificate and its key from it. iOS cannot read a .p12 exported without a password, and rejects a private key carrying its own passphrase: strip the passphrase or export a .p12.
Imported certificates never leave the device and never sync, so a connection set up on the Mac needs them imported again on each iPhone and iPad. See TablePro for iPhone and iPad.